


[Jul-2024] Download Real Fortinet NSE5_FCT-7.0 Exam Dumps Test Engine Exam Questions
New NSE5_FCT-7.0 exam dumps Use Updated Fortinet Exam
Fortinet NSE5_FCT-7.0 exam, also known as the Fortinet NSE 5 - FortiClient EMS 7.0 exam, is designed for IT professionals who want to demonstrate their expertise in managing endpoint security using FortiClient EMS 7.0. Fortinet NSE 5 - FortiClient EMS 7.0 certification exam covers a range of topics, including endpoint security management, endpoint compliance, endpoint protection, and endpoint telemetry.
Fortinet NSE5_FCT-7.0 is an industry-recognized certification exam that validates the knowledge and skills of network and security professionals in the deployment and management of FortiClient EMS 7.0. NSE5_FCT-7.0 exam is designed for those individuals who are responsible for managing network security infrastructure and ensuring the smooth operation of the FortiClient EMS 7.0 platform.
NEW QUESTION # 13
Refer to the exhibit.
Based on the CLI output from FortiGate. which statement is true?
- A. FortiGate is configured to pull user groups from FortiAuthenticator
- B. FortiGate is configured with local user group
- C. FortiGate is configured to pull user groups from AD Server.
- D. FortiGate is configured to pull user groups from FortiClient EMS
Answer: D
NEW QUESTION # 14
What does FortiClient do as a fabric agent? (Choose two.)
- A. Automates Responses
- B. Provides application inventory
- C. Creates dynamic policies
- D. Provides IOC verdicts
Answer: C,D
NEW QUESTION # 15
Refer to the exhibit.
Based on the settings shown in the exhibit which statement about FortiClient behavior is true?
- A. FortiClient quarantines infected files and reviews later, after scanning them.
- B. FortiClient copies infected files to the Resources folder without scanning them.
- C. FortiClient scans infected files when the user copies files to the Resources folder
- D. FortiClient blocks and deletes infected files after scanning them.
Answer: D
NEW QUESTION # 16
Refer to the exhibit.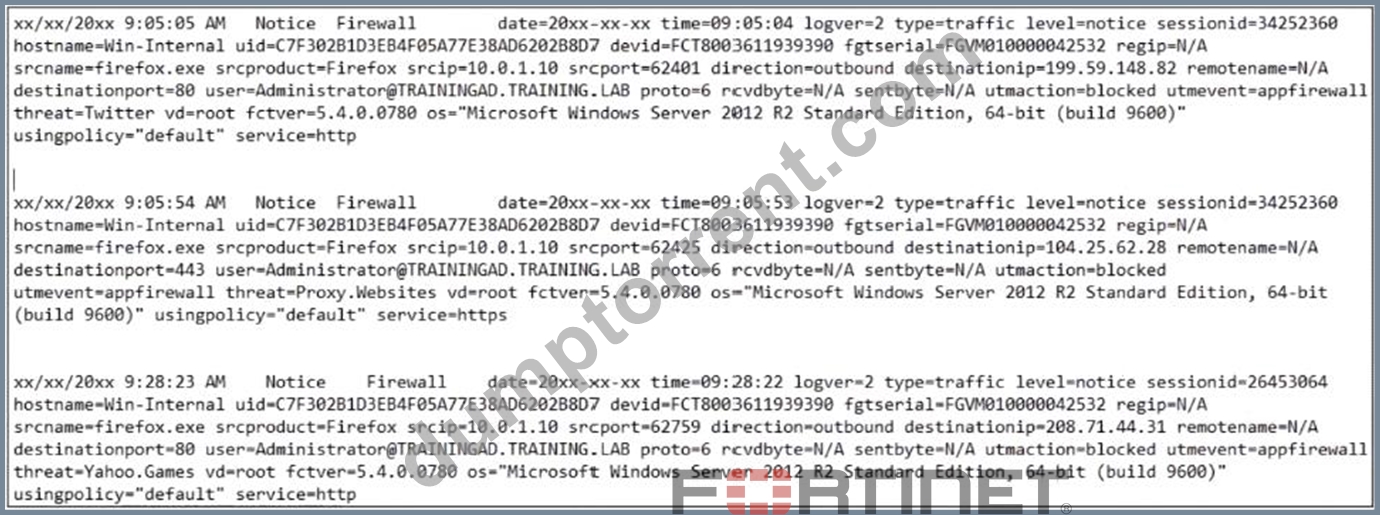
Based on the FortiClient logs shown in the exhibit which application is blocked by the application firewall?
- A. Internet Explorer
- B. Facebook
- C. Twitter
- D. Firefox
Answer: D
NEW QUESTION # 17
Refer to the exhibit.
Based on the FortiClient logs shown in the exhibit which application is blocked by the application firewall?
- A. Twitter
- B. Internet Explorer
- C. Facebook
- D. Firefox
Answer: A
Explanation:
Explanation
the Twitter was Blocked see line 5 in the exibit
NEW QUESTION # 18
Refer to the exhibit.
Based on the settings shown in the exhibit, which two actions must the administrator take to make the endpoint compliant? (Choose two.)
- A. Patch applications that have vulnerability rated as high or above
- B. Enable the webfilter profile
- C. Run Calculator application on the endpoint
- D. Integrate FortiSandbox for infected file analysis
Answer: A,C
NEW QUESTION # 19
Which two statements are true about ZTNA? (Choose two.)
- A. ZTNA provides a security posture check
- B. ZTNA manages access for remote users only
- C. ZTNA manages access through the client only
- D. ZTNA provides role-based access
Answer: A,D
NEW QUESTION # 20
Refer to the exhibit, which shows the endpoint summary information on FortiClient EMS.
What two conclusions can you make based on the Remote-Client status shown above? (Choose two.)
- A. The endpoint is classified as at risk.
- B. The endpoint has been assigned the Default endpoint policy.
- C. The endpoint is currently off-net.
- D. The endpoint is configured to support FortiSandbox.
Answer: B,C
NEW QUESTION # 21
Which two statements are true about the ZTNA rule? (Choose two. )
- A. It enforces access control
- B. It applies security profiles to protect traffic
- C. It redirects the client request to the access proxy
- D. It defines the access proxy
Answer: A,B
Explanation:
"A ZTNA rule is a proxy policy used to enforce access control. ZTNA tags or tag groups can be defined to enforce zero trust role based access. Security profiles can be configured to protect this traffic."
"ZTNA rules help control access by defining users and ZTNA tags to perform user authentication and security posture checks. And just like firewall policies, you can control the source and destination addresses, and apply appropriate security profiles to scan the traffic." https://docs.fortinet.com/document/fortigate/7.0.0/ztna-deployment/899992/configuring-ztna-rules-to-control-access
NEW QUESTION # 22
An administrator needs to connect FortiClient EMS as a fabric connector to FortiGate. What is the prerequisite to get FortiClient EMS to connect to FortiGate successfully?
- A. Revoke and update the FortiClient EMS root CA.
- B. Import and verify the FortiClient client certificate on FortiGate.
- C. Import and verify the FortiClient EMS root CA certificate on FortiGate
- D. Revoke and update the FortiClient client certificate on EMS.
Answer: C
Explanation:
Explanation
The FortiClient EMS root CA certificate needs to be imported and verified on the FortiGate appliance. This allows the FortiGate to trust the certificate authority (CA) used by FortiClient EMS for issuing client certificates. By importing and verifying the root CA certificate, FortiGate can establish a secure connection with FortiClient EMS and validate the authenticity of the client certificates presented during the connection process.
NEW QUESTION # 23
Which two third-party tools can an administrator use to deploy FortiClient? (Choose two.)
- A. Microsoft SCCM
- B. QR code generator
- C. Microsoft Active Directory GPO
- D. Microsoft Windows Installer
Answer: A,C
NEW QUESTION # 24
Why does FortiGate need the root CA certificate of FortiClient EMS?
- A. To trust certificates issued by FortiClient EMS
- B. To update FortiClient client certificates
- C. To sign FortiClient CSR requests
- D. To revoke FortiClient client certificates
Answer: A
Explanation:
Explanation
FortiGate needs the root CA (Certificate Authority) certificate of FortiClient EMS in order to trust and validate certificates that are issued by FortiClient EMS. The root CA certificate acts as a trusted authority that verifies the authenticity and integrity of certificates issued by FortiClient EMS.
NEW QUESTION # 25
Refer to the exhibit.
Which shows multiple endpoint policies on FortiClient EMS.
Which policy is applied to the endpoint in the AD group trainingAD?
- A. The Training policy
- B. The Sales policy
- C. Both the Sales and Training policies because their priority is higher than the Default policy
- D. The Default policy because it has the highest priority
Answer: C
NEW QUESTION # 26
Which statement about FortiClient comprehensive endpoint protection is true?
- A. lt helps to safeguard systems from advanced security threats, such as malware.
- B. It helps to safeguard systems from data loss.
- C. It helps to safeguard systems from email spam
- D. It helps to safeguard systems from DDoS.
Answer: A
Explanation:
FortiClient provides comprehensive endpoint protection for your Windows-based, Mac-based, and Linuxbased desktops, laptops, file servers, and mobile devices such as iOS and Android. It helps you to safeguard your systems with advanced security technologies, all of which you can manage from a single management console.
NEW QUESTION # 27
Which two VPN types can a FortiClient endpoint user inmate from the Windows command prompt? (Choose two)
- A. L2TP
- B. PPTP
- C. SSL VPN
- D. IPSec
Answer: C,D
NEW QUESTION # 28
When site categories are disabled in FortiClient webfilter and antivirus (malicious websites), which feature can be used to protect the endpoint from malicious web access?
- A. Real-time protection list
- B. Web exclusion list
- C. FortiSandbox URL list
- D. Block malicious websites on antivirus
Answer: B
NEW QUESTION # 29
Which component or device shares ZTNA tag information through Security Fabric integration?
- A. FortiGate Access Proxy
- B. FortiClient EMS
- C. FortiGate
- D. FortiClient
Answer: B
NEW QUESTION # 30
Refer to the exhibit.
Based on the logs shown in the exhibit, why did FortiClient EMS fail to install FortiClient on the endpoint?
- A. The FortiClient antivirus service is not running
- B. The remote registry service is not running
- C. The task scheduler service is not running.
- D. The Windows installer service is not running
Answer: C
NEW QUESTION # 31
Refer to the exhibit.
An administrator has restored the modified XML configuration file to FortiClient and sees the error shown in the exhibit.
Based on the XML settings shown in the exhibit, what must the administrator do to resolve the issue with the XML configuration file?
- A. The administrator must change the file size
- B. The administrator must save the file as FortiClient-config conf.
- C. The administrator must use a password to decrypt the file
- D. The administrator must resolve the XML syntax error.
Answer: D
NEW QUESTION # 32
......
Pass Your NSE5_FCT-7.0 Dumps as PDF Updated on 2024 With 51 Questions: https://braindumps2go.dumptorrent.com/NSE5_FCT-7.0-braindumps-torrent.html